It Calls

  • Subscribe to our RSS feed.
  • Twitter
  • StumbleUpon
  • Reddit
  • Facebook
  • Digg

Thursday, 10 November 2011

The Active Directory integrated DNS zone _msdcs.domain.com was not found

Posted on 07:38 by Unknown
Error Reported in Event Viewer or DNS Best Practices Analyzer.

"The Active Directory integrated DNS zone _msdcs.domain.com was not found"

This error might appear in environments and domains that were already built back in the days of windows 2000 or Windows 2003. By default, before windows server 2003 SP1, there was no independent _msdcs.domain.com zone in the DNS console. When the domain was originally created under Windows 2000 or Windows 2003, there was only a _msdcs folder under the domain.com zone which could also provide the resolution for _msdcs.domain.com zone. After windows server 2003 SP1, when you create a zone such as domain1.com, there is an independent _msdcs.domain1.com zone which is the delegation of the original _msdcs folder. This _msdcs will highly benefit the DNS replication.

What is the _msdcs Zone?
According to Microsoft documentation/definition:

“Microsoft-specific subdomain enables location of domain controllers that have specific roles in the Active Directory domain or forest. Resource records for the DNS root domain of a new Active Directory forest are stored in a _msdcs zone instead of a subdomain, and that zone is stored in the forest-wide application directory partition.”
This Zone will host only DNS SRV records that are registered by Microsoft-based services as well as the globally unique identifier (GUID) for all domains in the forest and a list of GC servers in your forest/domain.


DNS support for AD guide
http://technet.microsoft.com/en-us/library/cc759550(WS.10).aspx

The Steps needed to resolve these issues are as follows:
1.     Manually created _msdcs.domain.com zone

·         Open DNS console, right-click “Forward Lookup Zones”, click “New Zone”, manually create new zone _msdcs.Domain.com, please select primary zone and check “Store the zone in Active Directory” on the page of Zone Type.
Manual creation of DNS Zone


2.     After that, please check if _ msdcs.Domain.com has been created and the records are correct. If not continue with the next step.

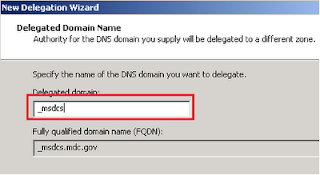
3.     Create a delegated _msdcs zone under the domain.com and delegate it to the _msdcs.domain.com zone. Right-click “Domain.com”, click “New Delegation”, please type _msdcs in the Delegated domain text box

DNS new delegation wizard


4.     Click Add button to type DNS server’s IP address.
5.     Stop and restart NETLOGON and DNS Service.

Email ThisBlogThis!Share to XShare to FacebookShare to Pinterest
Posted in Active Directory | No comments
Newer Post Older Post Home

0 comments:

Post a Comment

Subscribe to: Post Comments (Atom)

Popular Posts

  • Error 0x803100B7 Group Policy settings require the creation of a startup PIN, but a pre-boot keyboard is not available on this device
    I Purchased few weeks ago the Microsoft Surface Pro tablet, its a very nice production tablet that really enables remote users to run their ...
  • Surface 2 RT Bitlocker Recovery Key problem is fixed
    Windows Surface 2 RT comes already pre-setup with Bitlocker encryption, the user don't need to do anything to enable it or set/type a pa...
  • Two DNS Records with same IP Address. Aging and Scavenging problems with DHCP Lease duration !!
    Aging and Scavenging is very crucial and important for Active Directory Integrated zone, it should be carefully planned and configured. We r...
  • DNS64 Not Healthy after Applying UAG SP2
    For those who missed the latest news on UAG, Microsoft released UAG SP2 early this month. For what is new in Microsoft UAG SP2 please check ...
  • How to Publish New Certificate Revocation List (CRL) from Offline Root CA to Active Directory and Inetpub
    Its highly recommended when building your Microsoft PKI (Public Key Infrastructure) to have your Root CA offline after issuing the Enterpris...
  • How to Manually Delete Old/Empty WSUS computer Group from Database
    Recently i was trying to delete/Remove one of the old computer groups under WSUS Console - Computers - All Computers. This Group was an old ...
  • DHCP Superscope Keeps reverting back after Deletion
    I passed by this experience after the deletion of a DHCP superscope where the Superscope reverts back after the DHCP server is rebooted or a...
  • Troubleshooting Direct Access Teredo connectivity on Forefront UAG 2010
    I encountered a problem on one of my installations for DirectAccess where all the clients were able to connect to DirectAccess using HTTPS o...
  • RemoteApp and Web Application ICON Customization in UAG 2010 Portal
    UAG 2010 Portal customization is one of the key strengths in the UAG system. The Customization of UAG is based on the Custom Update concept,...
  • DNS64 Not Healthy after Applying UAG SP1 Update 1 Rollup 1
    After applying the latest Rollup 1 for UAG SP1 Update 1 released on Jan 12, 2012 I noticed that the DNS64 is unhealthy under the Direct Acce...

Categories

  • Active Directory
  • Bitlocker
  • DirectAccess
  • Hyper-V
  • Lync
  • PKI
  • SQL
  • System Center
  • UAG
  • WSUS

Blog Archive

  • ►  2014 (1)
    • ►  January (1)
  • ►  2013 (27)
    • ►  December (5)
    • ►  November (4)
    • ►  October (2)
    • ►  September (1)
    • ►  August (4)
    • ►  July (4)
    • ►  May (1)
    • ►  April (2)
    • ►  March (3)
    • ►  February (1)
  • ►  2012 (25)
    • ►  December (2)
    • ►  November (3)
    • ►  October (3)
    • ►  September (2)
    • ►  August (2)
    • ►  July (2)
    • ►  May (2)
    • ►  April (1)
    • ►  March (3)
    • ►  February (2)
    • ►  January (3)
  • ▼  2011 (5)
    • ►  December (2)
    • ▼  November (3)
      • UAG Direct Access IP-HTTPS fail with SAN Certificate
      • The Active Directory integrated DNS zone _msdcs.do...
      • Troubleshooting Event ID 1058, Group Policy gpt.ini
Powered by Blogger.

About Me

Unknown
View my complete profile